Detect human insider risk at the endpoint
Continuous endpoint screening against verified File Risk Indicators, integrated into the security workflows you already use.
Continuous endpoint screening against verified File Risk Indicators, integrated into the security workflows you already use.
Continuous endpoint detection built on verified intelligence
Offering highlights
Challenge
Traditional security controls provide extensive visibility into malware, compromised credentials, data exfiltration and other technical risks. But some forms of human-driven risk can remain outside their scope.
Detection Services add specialized intelligence at the endpoint to help organizations identify matches against known File Risk Indicators.
Approach
File Detection for Endpoints continuously screens supported file activity directly on the endpoint.
Matching takes place locally against verified File Risk Indicators from NetClean intelligence, with detection designed to operate both online and when an endpoint is temporarily offline.
Outcome
When a match is identified, ProActive makes relevant detection and endpoint context available for assessment and investigation.
Alerts can be securely reviewed in Alert Vault, forwarded into existing SIEM/SOAR workflows, or both.
Audience
Detection Services are designed for organizations that want specialized human insider risk intelligence without replacing the security infrastructure already in place.
Alerts and context can support SOC teams, insider risk functions, investigations, compliance processes and other established response workflows.
001
Workstation Event Screening runs in the background and is triggered by real-time file events on supported endpoints.
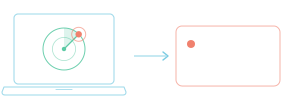
Files are matched locally against verified File Risk Indicators. When a match is identified, ProActive records a detection event.
002
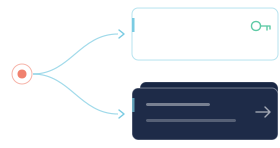
Relevant alerts can be securely reviewed in ProActive Alert Vault, forwarded into existing SIEM, SOAR and security workflows, or both.
Alerts include relevant detection and endpoint context to support assessment and investigation.
Alert information can be incorporated into existing security, investigation and response processes.
See how Detection Services fit into your security ecosystem.
Let’s talkALERT HANDLING
ProActive Alert Vault provides secure storage and controlled access for sensitive alerts generated by File Detection for Endpoints.
Use it alongside Alert Forwarding into existing security platforms, or as the primary surface for reviewing alerts.
INTEGRATION-FIRST
Frequently answered questions
Discover
Analysis Services

Intelligence Services
Contact us
Explore how NetClean ProActive can bring specialized human insider risk intelligence into your existing security environment.


